

Most “leave Splunk” write-ups turn into feature matrices. The job you actually have is narrower: keep critical logs searchable, recreate the alerts that wake people up, and stop paying for a stack you no longer want to operate. This guide walks a Splunk → Logit.io cutover onto Hosted OpenSearch (or a log management stack when that is the better landing pad) — shippers, indexes, Discover, monitors, managed limits, and honest parity gaps. For positioning context only, see the Splunk alternative page; the body below is the migration path, not another top-N list.
Contents
- When Splunk→OpenSearch migration is the real job
- Pick the Logit landing pad: log stack vs Hosted OpenSearch
- Replace forwarders with Logit-supported shippers
- Indexes, index patterns, and Discover fields
- Alerts: OpenSearch monitors vs saved-search muscle memory
- Managed Hosted OpenSearch limits you must plan for
- Cost framing with per-node OpenSearch pricing
- Failure modes / common mix-ups
- Get started
When Splunk→OpenSearch migration is the real job
Migration is the right framing when cost, licensing friction, or operational control — not a missing checkbox — is why you are leaving. You care about which hosts still run Universal Forwarders, which indexes hold the incidents you page on, and which saved searches must fire on day one. Feature comparison pages do not shrink that backlog.
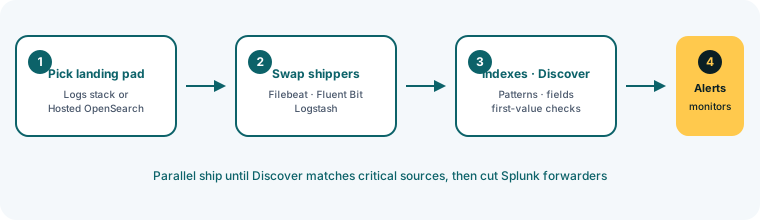
Treat the project as parallel ingest, prove Discover coverage for the critical sources, recreate the alerts that matter, then retire Splunk forwarders. Do not plan a big-bang “export every historical bucket” unless compliance forces it; most teams need continuity of new events more than a perfect archive copy.
Pick the Logit landing pad: log stack vs Hosted OpenSearch
Logit.io exposes OpenSearch in two shapes. A log management stack is the shipper-first path: Filebeat, Fluent Bit, Logstash, and friends land logs for Discover, dashboards, and operational alerting. A dedicated Hosted OpenSearch cluster is cluster-first — you provision nodes, connect clients to the endpoint, and treat OpenSearch as the search/analytics backend.
If success means “replace Splunk logging for ops,” start with a log stack (log management plans start from $25/mo annual). If success means “OpenSearch as a managed search cluster with your own indexes and APIs,” create a dedicated cluster via Creating an OpenSearch cluster. The decision walkthrough lives in Log stack vs Hosted OpenSearch; those are the two options.
Replace forwarders with Logit-supported shippers
Universal Forwarders do not magically become OpenSearch clients. On Logit you point supported shippers at the stack endpoints from Settings → Endpoints:
- Filebeat — file and many host log paths; closest mental model to “tail files and ship.”
- Fluent Bit — lightweight agents, Kubernetes DaemonSets, and multi-input collectors.
- Logstash — richer parsing, routing, and filter pipelines when you need transform-before-index.
OpenTelemetry Collector paths are documented under OpenTelemetry getting started when your estate already standardizes on OTel — otherwise prefer Filebeat or Fluent Bit for a Splunk forwarder replacement. New to shipping anything on Logit? Pair this cutover with first logs on Logit.io so the first source proves end-to-end before you scale hosts.
Practical cutover: dual-ship a canary host or namespace into Logit while Splunk still receives the same stream. Confirm volume and fields in Discover, then flip the remaining fleet. High-ingest clusters should also skim OpenSearch high-ingestion settings before you point every forwarder-replacement at once.
Unlock complete visibility with hosted ELK, Grafana, and Prometheus-backed Observability
Indexes, index patterns, and Discover fields
Splunk “indexes” and OpenSearch indexes share a name and little else. On Logit, events land in OpenSearch indexes (often time-based or source-shaped via Logstash). In OpenSearch Dashboards you create an index pattern (for example logs-*) that Discover uses to search across matching indexes. First value is not a perfect SPL port — it is: pick the pattern, set the time field, run a simple query for a known host or app, and confirm the fields you page on are present and typed.
SPL habits to drop early: piping for field extraction belongs in Logstash filters or ingest-time parsing, not in every interactive query. Prefer structured fields at ship time so Discover filters and aggregations stay cheap. Map a short “must-have” field list from your Splunk saved searches (host, sourcetype-equivalent, severity, service) and verify those fields before you recreate dashboards.
Alerts: OpenSearch monitors vs saved-search muscle memory
Splunk saved-search alerts do not import as OpenSearch monitors. On Logit, recreate paging rules with OpenSearch Alerting monitors: pick a data source, define the query or filter, set a trigger threshold, and attach a notification action. Start with the handful of alerts that page humans; leave noisy informational searches for a second wave.
Honest parity gaps: complex SPL (subsearches, join-heavy correlation, lookup-driven enrichment at alert time) will not 1:1 onto a single monitor query. Move enrichment into the pipeline where possible, or accept a simpler trigger plus a Discover runbook. Do not promise “every saved search becomes a monitor unchanged” — inventory severity and rebuild the top tier deliberately.
Managed Hosted OpenSearch limits you must plan for
Hosted stacks expose the OpenSearch REST API for search, indexing, and day-two index work, but they are not a self-managed cluster you can re-topology at will. Read managed stack limitations before you script a Splunk-era automation habit onto the endpoint.
Plan around: no customer security-plugin admin via /_plugins/_security; no adding/removing nodes or installing arbitrary plugins via API; snapshot/restore lifecycle is platform-managed; some cluster settings are rejected or overridden. Practical OpenSearch defaults still apply — for example index.max_result_window at 10,000 hits per search — so large exports need scroll or batched patterns, not a single giant result window. Contact support for topology or recovery cases the dashboard does not expose.
Cost framing with per-node OpenSearch pricing
Dedicated OpenSearch pricing is per node: published developer tiers start at $45.52/node/mo (annual). Cluster cost scales with node count × tier — two DEV-1-1-10 nodes are two × that rate on the published table, rather than a custom TCO estimate. Confirm current node sizes on the live pricing page when you size for retention and ingest.
If you chose a log management stack instead of a dedicated cluster, price log retention and ingestion on log plans (from $25/mo annual). Keep OpenSearch per-node rates for dedicated clusters; the $25/mo log-plan starting price is not Hosted OpenSearch cluster pricing. Metrics (from $12/mo) and APM (from $20/mo) only enter the bill when those products are in scope.
Failure modes / common mix-ups
- Wrong landing pad. Building custom search indexes on a Logs stack — or shipping only ops logs to a dedicated cluster without a log pipeline story — creates the wrong operating model. Re-read the stack-type choice before you scale shippers.
- Forwarders still only talking to Splunk. Dual-ship until Discover shows the canary; then cut. Leaving half the fleet on Universal Forwarders alone is not a migration.
- Expecting SPL equivalence on day one. Prove fields and time range in Discover first; port queries after the data shape is stable.
- Alert big-bang. Recreate paging monitors first. Porting hundreds of informational saved searches before ingest is stable wastes the cutover window.
- Ignoring managed limits. Scripts that assume self-managed security APIs, plugin installs, or snapshot repos will 403 — that is platform design, not a misconfigured password.
- Pricing mix-up. $45.52/node/mo is Hosted OpenSearch; $25/mo is the log management starting price. Mixing them in a business case sinks trust with finance.
Get started
Open a 14-day trial, choose log stack or dedicated Hosted OpenSearch from the decision above, and create the cluster (or stack) with the docs for creating an OpenSearch cluster when you need the dedicated path. Point one Filebeat, Fluent Bit, or Logstash canary at Settings → Endpoints, confirm Discover, stand up the first OpenSearch Alerting monitor, then scale shippers and retire Splunk forwarders source by source. Size dedicated nodes on OpenSearch pricing from $45.52/node/mo when the landing pad is Hosted OpenSearch.